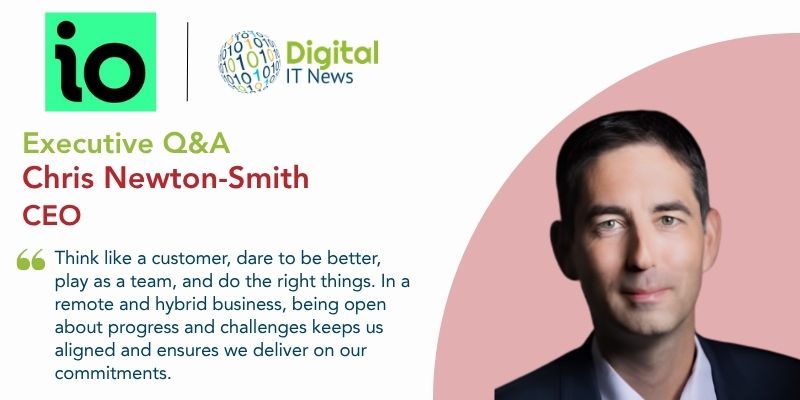
Chris Newton-Smith has more than 20 years of experience in B2B software, working in the mobile, digital, and hospitality markets. He is the CEO at IO (previously known as ISMS.online), which provides a comprehensive solution to robust and scalable governance, risk, and compliance for more than 1,000 companies around the world. Prior to IO, Chris was the Chief Operating Officer (COO) at Boku, a global network of localized payment solutions. Chris led Technology, Operations, IT & Information Security, Risk & Compliance, and People Operations. Boku built a network of digital wallets and A2A connections processing more than $10B in payments volume for the world’s largest digital merchants, including Google, Meta, and Amazon.
Can you share the most interesting story that happened to you since you started your career, especially one that shaped your leadership approach at your current company?
I joined Redknee in Toronto from BlackBerry when it was a start-up of approximately 10 people. As we won our first mobile telecoms customers in Europe, I moved from Canada to Munich to lead our European sales. Over the following years, we grew the business substantially across Europe and then in the Middle East and Africa under my leadership.
We were competing against very large, well-funded companies such as Ericsson and Nokia. We couldn’t outspend them, so we won by focusing. We concentrated on the customer problems we could solve best, and we made sure we delivered a high-quality product, especially well-suited for our target customers.
Redknee grew to become a global leader in telecoms, working with more than 200 carriers in 100 countries. Those lessons translate directly to IO (formerly ISMS.online). Staying close to our target customers, focusing on what we do best and delivering quality are how we compete and grow today.
What initially brought you to this specific career path, and how did it lead to your role in this company?
My path to IO came through payments. As COO at Boku, I helped build a payment processing network for local payment methods, growing from one mobile wallet to more than 50 mobile wallets and account-to-account connections. We worked with the world’s largest digital merchants, including Amazon, Google, and Meta.
To do that, we had to build locally regulated payments businesses in markets including the EU, UK, Hong Kong, India and Singapore. Every new market brought new requirements for information security, data protection, and compliance. We expanded our compliance and security teams, achieved ISO 27001 certification, and I learned firsthand how much effort it takes to build a compliance program that scales with the business.
That experience changed how I saw compliance and business resilience. It was the foundation that allowed us to grow, win enterprise customers, and earn the trust of regulators. When I considered my next role, I wanted to help other organizations solve that same challenge. IO, with its platform and team of domain experts, was the natural fit.
What makes your company stand out from competitors in the market? Can you share an example that highlights this?
Many providers in our market focus on getting organizations certified as quickly as possible through automation. We think that misses the point. A certificate shows that controls existed at a point in time. It doesn’t prove that a business can withstand what comes next.
Compliance done fast can leave organizations compliant on paper but vulnerable in practice. Controls are put in place quickly enough to pass an audit, but not long enough to become part of how the business actually runs. Our research found that UK cybersecurity managers see continuous monitoring of controls as one of the strongest indicators of business resilience, and 45% say human expertise is still essential to judge whether automated compliance outputs are relevant and accurate.
That is where IO is different. We focus on business resilience, not just certification. IO supports more than 1,100 customers by combining a powerful platform with proven processes and a team of compliance experts.
We help organizations embed information security, data privacy and AI governance into day-to-day operations, so compliance becomes a capability they build rather than a project they complete. The result is a business that can absorb new requirements, withstand disruption, and keep earning the trust of customers, partners, and regulators.
Are you working on any exciting new products or projects? How do you think this innovation will positively impact your customers?
Our biggest focus is the Resilience Loop, which connects the three areas at the heart of business resilience: information security, data privacy, and AI governance. Most of our customers have core standards needs in each area, such as ISO 27001, ISO 27701 and ISO 42001.
On top of that, they are facing a growing wave of new requirements: regulations and legislation such as NIS2, DORA and the EU AI Act, sector-specific requirements in markets like financial services and healthcare, and security demands from their own customers.
Managing each of these separately creates significant complexity and duplicated effort. That is why we are bringing Unified Compliance to the market. It gives customers a common control set, so they can implement a control once and use it to demonstrate compliance across multiple standards and regulations.
Our partnership with the Secure Controls Framework helps us map requirements from a broad range of frameworks to that common set of controls.
The impact for customers is simplicity and confidence. New requirements are absorbed into an existing structure rather than arriving as a new project, and customers can show procurement teams, regulators and partners that compliance is embedded in how their business runs.
What was the tipping point for your company’s recent success? Was there a change in strategy or approach that others might learn from?
The tipping point has been focus. We have concentrated on organizations where compliance and resilience are core to operating successfully, often because of regulatory requirements. These include businesses in markets such as financial services and health tech, where strong information security, data privacy, and AI governance are essential to winning customers and meeting regulators’ expectations.
For these organizations, compliance isn’t a one-off project. Their requirements keep evolving as they grow, enter new markets, and adopt new technologies. So, we have focused on building long-term partnerships with our customers and investing in our product to make sure we move with them as their needs change, from a first certification to mature, multi-framework programs.
The lesson for others is that focus creates momentum. Being clear about which customers you serve best, and committing to them for the long term, makes it much easier to prioritize investment and deliver real value. It also means being willing to let go of good opportunities to make room for the best ones.
Can you share a significant challenge your company faced and how you overcame it? What key lesson did that experience provide?
A challenge for the company was expanding beyond information security to include data privacy and AI governance. Our customers’ needs have broadened over the past years. Organizations that came to us for ISO 27001 now also need to manage GDPR, ISO 27701 and, increasingly, ISO 42001 and the EU AI Act. We moved early, and IO was one of the first in the world to help customers achieve ISO 27701, for data privacy, and ISO 42001 for AI management systems.
The risk of expanding like this is creating separate silos for each new area, which only adds to customers’ complexity. Solving that problem has driven our product roadmap for the past year. It has led us to bring Unified Compliance to market, which we believe is a unique way of helping customers manage information security, privacy and AI governance together through a common set of controls.
The key lesson is to expand from your strengths and let customer challenges shape your roadmap. New requirements are much easier to address when they build on foundations you and your customers already trust.
In just a few words, what differentiates your leadership role from others in the company? What impact does this have on company culture or product success?
Clarity, customer focus, and accountability. Our vision is to set the standard for business resilience, enabling strong information security, data privacy, and AI governance through our exceptional people, processes and platform. Our values guide how we get there:
Think like a customer, dare to be better, play as a team, and do the right things. I’m passionate about this space, and my role is to make sure we deliver that vision and those values for our customers over the long term. In a remote and hybrid business, being open about progress and challenges keeps us aligned and ensures we deliver on our commitments.
For more than 10 years, IO (formerly ISMS.online) has been helping companies big and small find their compliance confidence. The company believes that compliance should be a positive process that helps businesses grow. Over the past 10 years, IO has empowered more than 65,000 users globally to achieve their compliance needs, has helped 100% of its customers achieve ISO 27001 certification on their first attempt, and supports more than 100+ global frameworks and regulations in one place.
Related News:
Back to School Cybersecurity Advice
Leostream Launches Leostream Cloud for Secure Remote Access Without VPNs