Tanium introduced new Security Operations capabilities powered by Tanium Atlas, its autonomous operating system, designed to help customers create a self-driving SOC that can operate autonomously within operator-defined controls. The expanded portfolio provides IT and security teams with deeper detection, flexible response capabilities, and AI-native threat hunting to investigate, contain, and remediate threats more quickly using real-time endpoint intelligence instead of outdated, pre-ingested data.
Enterprise security teams are losing ground in the AI era. Exploited vulnerabilities have overtaken stolen credentials as the leading breach vector for the first time, attackers are weaponizing flaws faster than defenders can patch them, and the global mean time to contain a breach still stands at 247 days. Most IT and security operators are investigating threats with fragmented tools and pre-ingested telemetry that can be hours old, requiring manual correlation before any remediation can begin. Tanium Security Operations closes that gap by enabling IT and security operators to reason over the endpoint as it exists right now, extend existing SIEM and EDR investments, and act from a single platform.
“Security teams don’t need another tool that generates more alerts. They need the truth about what’s happening on their endpoints right now, and the power to act on it before an attacker does,” said Harman Kaur, chief technology officer at Tanium. “Tanium Atlas brings live endpoint intelligence and agentic AI together so operators can detect what is abnormal, investigate it in context, and respond immediately. The customer sets the rules and autonomy runs the workflow.”
Detection, Response, and Hunting — Built on Live Endpoint Visibility
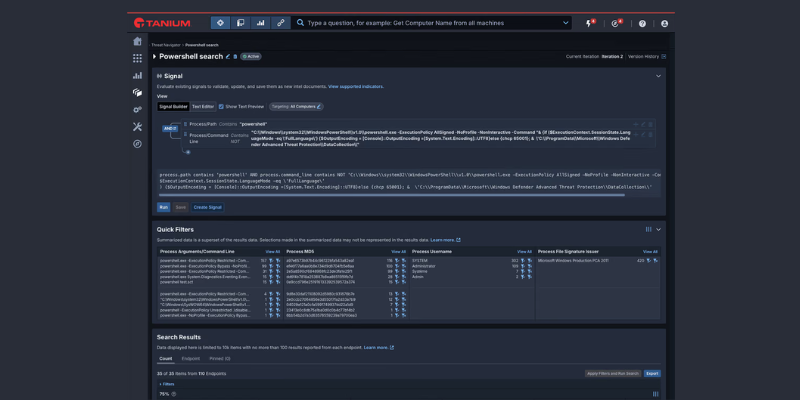
Tanium Security Operations is built on the Tanium Autonomous IT Platform, combining real-time visibility across managed endpoints with the ability to act safely at speed and scale. The expanded portfolio is organized around three pillars:
- Detection depth and data fidelity: Tanium detects threats against live endpoint state, not aged data. New Endpoint Drift surfaces abnormal behavior against historical baselines, and Insights Engine detects advanced in-memory techniques, delivering faster, more focused hunting and better prioritization of suspicious activity across the fleet, and faster delivery of protection against advanced techniques.
- Diverse response: Tanium pairs detection with a full spectrum of response options executed directly on the endpoint, from quarantining hosts to collecting forensic evidence. A new Federated SOC architecture lets operators work independently on one platform, backed by a modernized Windows quarantine built for agentic SOC actions and safer multi-team operations.
- AI-native hunting: Tanium Atlas helps IT and security operators investigate threats, prioritize alerts, and determine next steps. New Alert Prioritization and Triage ranks the queue and recommends whether to dismiss, escalate, hunt, or contain, delivering faster alert-to-decision time, less analyst fatigue, and fewer low-value alerts. New SecOps dashboards and templates make expert-level hunting faster to scale.
Tanium combines historical evidence with live endpoint data, giving Tanium Atlas the context to validate alerts, determine blast radius, and uncover root cause. New integrations deepen that context further: Google Threat Intelligence in Tanium SecOps brings premium intelligence directly into investigation and hunting workflows, while multi-provider reputation intelligence from five leading providers reduces false positives and accelerates triage. IT and security operators can move directly from investigation to containment and remediation without switching platforms.
For organizations that need to go further to minimize organizational risk, Tanium HuntIQ combines security research, expert threat hunters, and agentic AI built on Tanium Atlas. Tanium HuntIQ experts work directly within customer environments to identify threats, strengthen detections, and support incident response, with findings feeding back into the platform, so every subsequent hunt starts smarter.
To learn more about Tanium Security Operations, available now, visit the website here.
Related News:
Agentic SOC: Exabeam Advances AI-Powered Security Operations
Cribl Launches Detect SIEM with Platform-First Approach to Security Operations