Cribl has introduced Cribl Detect, a SIEM built on the company’s open data platform to help security teams detect, investigate, and respond to threats while maintaining greater control over their telemetry. Cribl says the platform-first approach enables organizations to customize their SIEM around existing security operations while delivering the technology at up to 50% lower cost than competing offerings. The launch expands Cribl into the $8.2 billion SIEM market.
AI-generated attacks increase both the speed and sophistication of threats, putting pressure on security teams to detect and respond faster. Since Cribl Detect runs on the company’s agentic AI-powered platform, with built-in inference and an agentic runtime, it can move beyond static, rules-based detection.
Intelligence from Cribl’s AI security operations center (AI SOC) capabilities helps automate detection and investigation workflows, applying analytics closer to the data to surface high-fidelity, actionable signals, reduce noise, and prioritize the threats that matter most. Together, these capabilities help security teams find blind spots and improve security outcomes.
Security teams face difficult choices with today’s SIEMs
For years, security teams frustrated with their SIEMs have faced two flawed options. Legacy monolithic SIEMs offer integration without choice, forcing customers into one vendor’s schema, one vendor’s pricing model, and per-gigabyte economics that turn analysis into a tax. Newer “SIEM-less” stacks assembled on general-purpose data platforms offer choice without integration.
Teams get to pick their tools, but they also become the integrator, stitching together separate schemas, contracts, and pipelines themselves. Cribl Detect is designed to offer the best parts of both: the openness and customizability of a platform-first approach with the comprehensive out-of-the-box detection, investigation, and response capabilities of a purpose-built solution. This same platform approach powers Cribl’s expanding portfolio of solutions.
“Customers don’t want the SIEM they have today, and they don’t have the resources to build the SIEM they want,” said Clint Sharp, co-founder and CEO of Cribl. “With Cribl Detect we’ve taken a different approach that solves both problems – an out of the box SIEM experience built on a highly flexible platform specifically for telemetry that allows customers to adapt, mold, and even rebuild the SIEM for their specific needs. And because the platform natively integrates inference and an agentic runtime, Cribl Detect goes beyond rigid rules to catch fast-moving AI threats.”
Skip the “DIY” headaches
While a “do it yourself” approach to SIEM and security operations can sound appealing, enterprises are rarely prepared to build and support what they need. Cribl’s new way to SIEM offers an alternative that starts with the same telemetry that organizations already access using the Cribl platform they already trust, in open formats they can control.
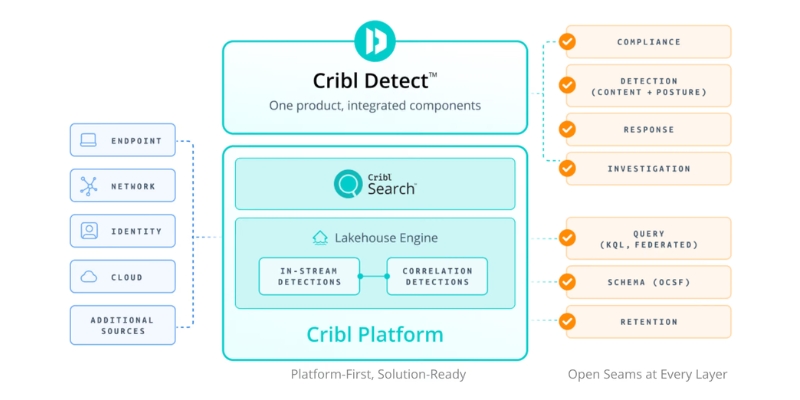
This means that Cribl Detect’s alerts, investigations, and analytics can run against data wherever it resides, rather than being confined or duplicated to a monolithic, single-vendor stack. With Cribl Detect, federation allows analysts to investigate across distributed telemetry in pipelines, data lakes, object stores, and existing tools. Cribl also applies detections in-stream as telemetry moves through the pipeline, bringing security logic to the data wherever it flows, getting the right signals moving earlier, so correlation and investigation can happen faster.
A key differentiator of Cribl Detect is that its detections and detection posture management (DPM), triage with AI security operations center (AI SOC), security orchestration/automation/response (SOAR), and compliance/governance capabilities all inherit access to any data available in the platform. This makes it possible to run the product without having to move historical data first.
“Cribl Detect brings together two capabilities that matter to practitioners: investigating across data they already control and identifying detection gaps, broken rules, and missing telemetry,” said Francis Odum, cybersecurity researcher at Software Analyst Cyber Research. “Building these capabilities into its existing data platform is a compelling direction for Cribl, giving security teams a path to modernize their SOC without creating another proprietary data silo.”
Built-In DPM and AI triage to accelerate incident response
Cribl Detect includes detection posture management that gives security teams a continuously updated view of what they are and aren’t detecting. Cribl Detect not only maps existing detections against MITRE ATT&CK techniques, surfacing coverage gaps, broken or noisy rules, and missing telemetry, but also provides recommendations and workflows for fast remediation.
Alongside rules-based detections, AI SOC intelligence powers automated detection techniques that catch threats rules alone would miss. AI-driven triage, investigation, and disposition technology then helps analysts move from alert to answer faster, without manually correlating data across tools.
Organizations that adopt Cribl Detect can expect lower total costs than incumbent SIEMs, since it is priced on infrastructure rather than an analysis tax. Read more here: https://cribl.io/blog/a-new-way-to-siem-starts-with-a-new-foundation/
For more information, visit: https://cribl.io/
Related News: